October 20, 2026
Hackers Are Inside Ivanti VPNs Right Now: CISA Orders an Emergency Patch
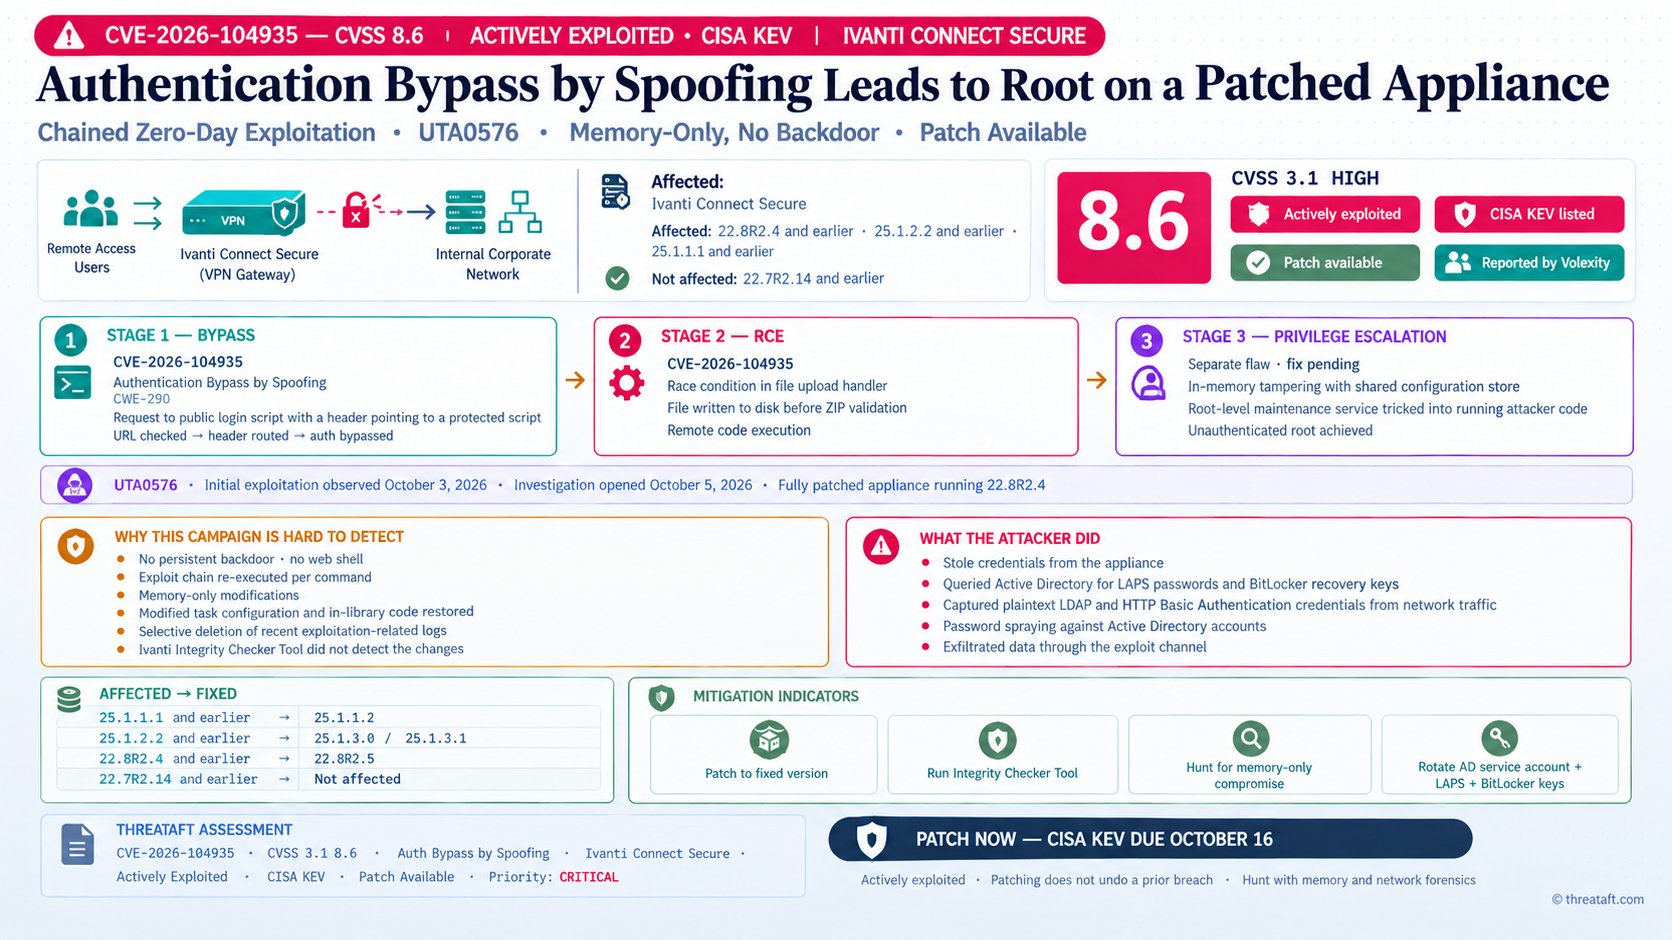
CISA is telling every organization running Ivanti Connect Secure to patch now. A zero-day flaw, CVE-2026-104935 (CVSS 8.6), lets a remote attacker with no credentials at all execute commands on the VPN appliance — and it was actively exploited since October 3, a full ten days before a patch existed. Federal agencies were given until October 16 to fix it.
Investigators at Volexity found one attacker, tracked as UTA0576, chaining the flaw with two others to reach root-level control of a fully patched appliance — then stealing Active Directory credentials and tampering with the appliance’s own logs to defeat Ivanti’s integrity checker. CISA warns that patching alone isn’t enough: any internet-facing appliance from the exploitation window should be treated as potentially compromised and investigated.